CYBERSECURITY ADVISORY AND MANAGED SERVICES
Secalyx helps growing technology companies understand exposure, meet customer expectations, and build security controls their teams can sustain.
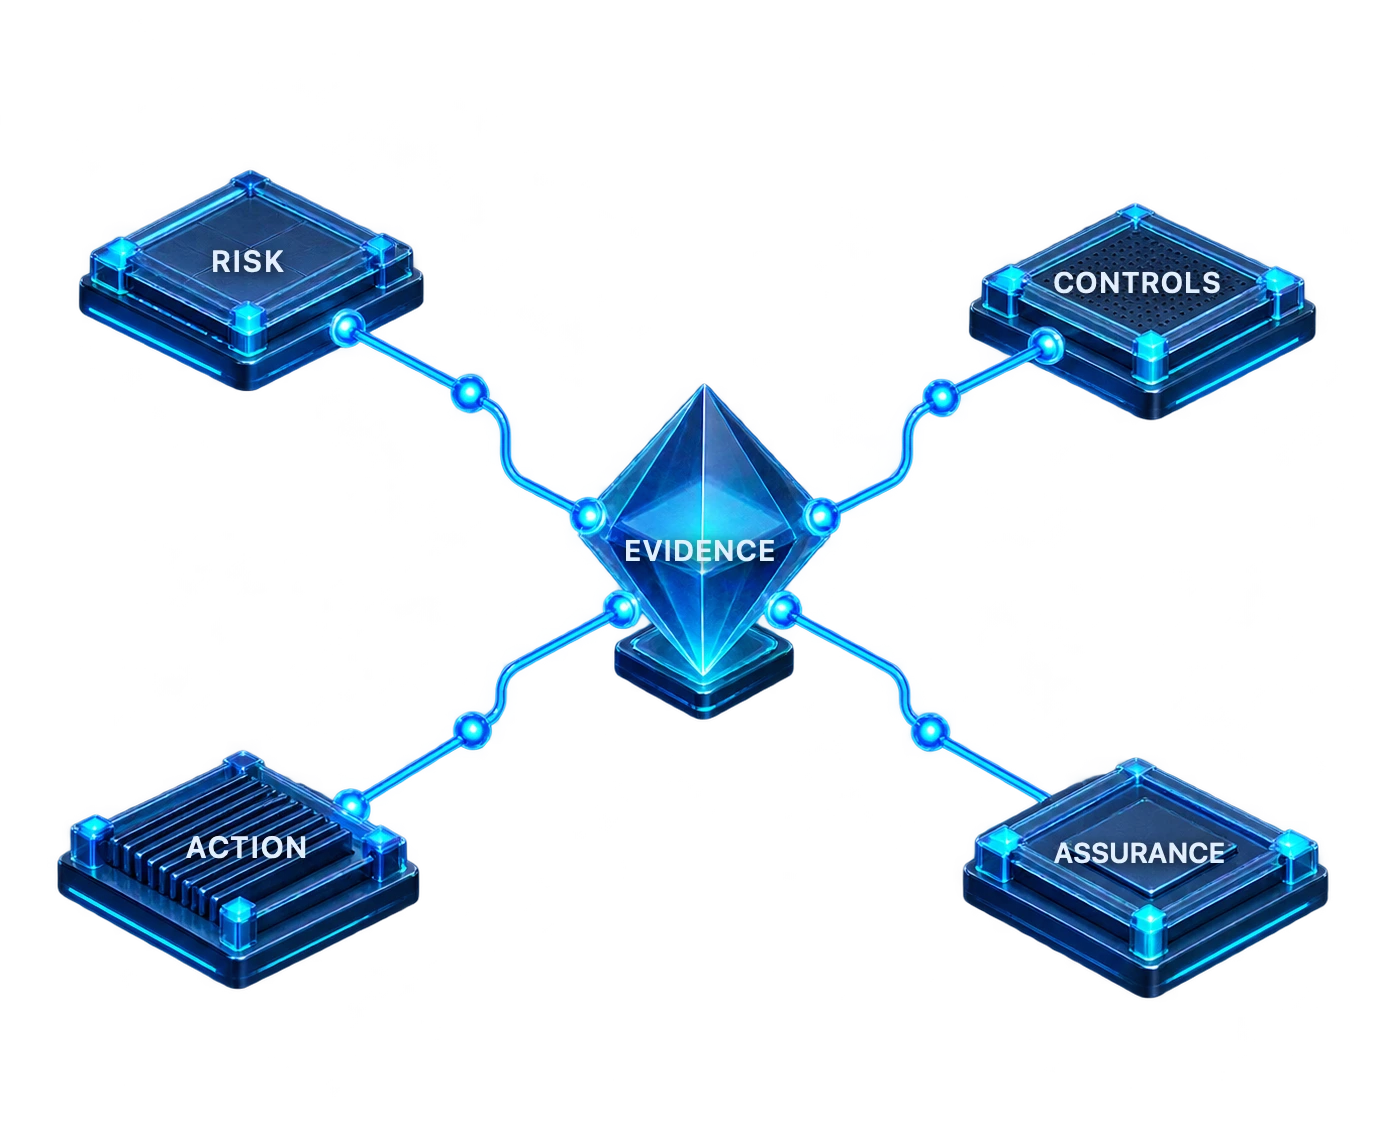
OUR WORKING PRINCIPLES
EVIDENCEExamined directly
SCOPEResponsibilities agreed first
RECOMMENDATIONSAppropriate to the business
HANDOVERKnowledge retained by the client
WHERE THE WORK BEGINS
A customer request, a control gap, and a regulatory obligation often land on the same small team in the same month. The work is to separate urgency from importance, and to establish what evidence is actually required before committing to anything.
01EXTERNAL DEMAND
A questionnaire arrives, or a contract clause does. Both ask for evidence of controls you may well run, but have never had to document in the shape being asked for.
02VISIBILITY GAP
Systems, responsibilities, and existing safeguards are each known in parts, by different people. Nobody has assembled the whole picture, so priority follows whoever asked most recently.
03OWNERSHIP GAP
The assessment ends and the findings are real, but nobody owns the controls afterward. Reviews slip, evidence goes stale, and the next customer request starts the cycle again.
Frameworks, standards and regulations
FOCUSED ADVISORY SERVICES
Choose a focused engagement, or combine related disciplines around one business outcome. Scope is defined before the work begins.
CONTINUITY AFTER THE PROJECT
Secalyx can help build the capability, share responsibility with your team, or operate agreed security controls. These are operating models, not fixed packages.
We establish the controls, documentation, routines, and skills, then transfer operation to your team.
Best if you are building internal capability.
Responsibility is divided deliberately: your team keeps context and access, Secalyx carries specific direction and operating discipline.
Best if you have a capable team with selected gaps.
Secalyx operates the agreed controls within the client’s stated business decisions, approvals, and internal accountability.
Best if defined controls need running continuity.
HOW AN ENGAGEMENT WORKS
The sequence is simple to understand and disciplined enough to audit. The exact evidence, responsibilities, and outputs are agreed for each engagement.
01
Clarify the business trigger, boundaries, and success criteria.
02
Review what exists, test key assumptions, and distinguish fact from assertion.
03
Sequence actions around material risk, customer need, and operating capacity.
04
Transfer a sustainable capability, or run the agreed security-control scope.

Founder & Principal Consultant
He holds CISSP (since 2009), CISM, CRISC, CISA, C|CISO, and CEH, and is a BSI-certified ISO/IEC 27001:2022 Lead Auditor and Lead Implementer.
Across a career spanning 25+ years, he has personally designed, built, and run cybersecurity and IT infrastructure from single-site environments to multi-city operations spanning Bengaluru, Mumbai, Delhi NCR, Pune, Indore, and international sites, supporting 5,000+ users.
He led security and technology programs that supported customer assurance assessments for Fortune 100 and Fortune 500 organizations across BFSI, healthcare, aviation, and other regulated environments. His current advisory work also includes data protection, security framework implementation, AI governance, and Fractional CISO leadership.
INSIGHTS
READY TO DISCUSS THE DECISION?
Share the pressure, requirement, or control question you are working through. A completed brief is not required.