Managed Cybersecurity
Secalyx runs your cybersecurity function within the scope agreed in the statement of work (SOW).
Best if you do not yet have an internal security function.

Cybersecurity advisory and managed services
Security your customers can verify, and your team can sustain.
Secalyx helps growing companies understand exposure, meet customer expectations, and build security controls with the evidence behind them.
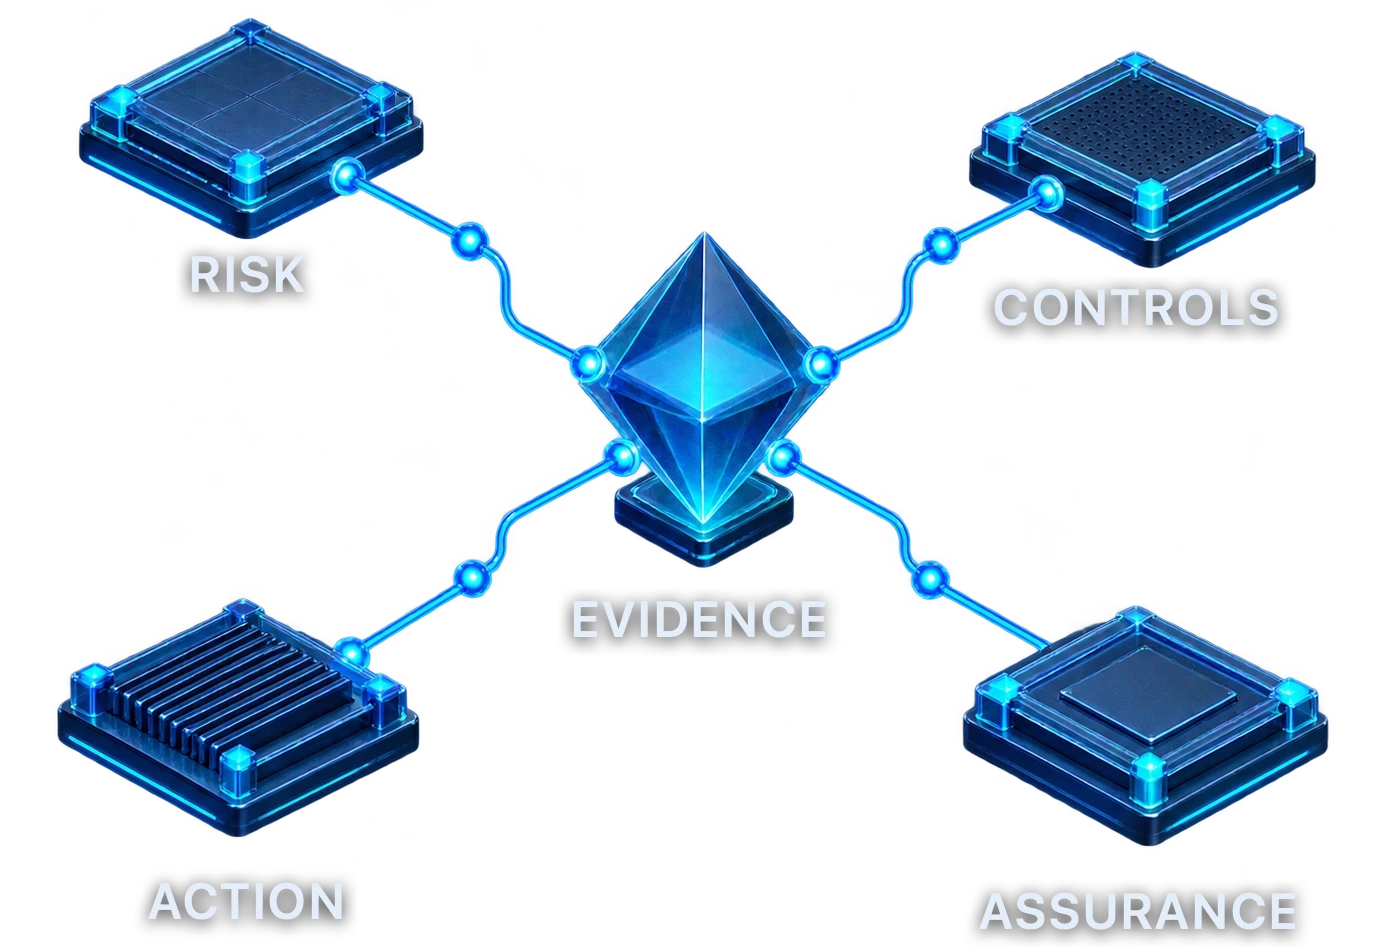
Examined directly
Responsibilities agreed first
Appropriate to the business
Knowledge retained by the client
Start here
A customer is reviewing our security
Managed Cybersecurity ServicesWe’re preparing for ISO/IEC 27001 or SOC 2
ISO 27001 Readiness SOC 2 ReadinessWe need ongoing security ownership
Managed Cybersecurity ServicesWe need senior security leadership
Fractional CISOWhere the work begins
A customer request, a control gap, and a regulatory obligation often land on the same small team in the same month. The work is to separate urgency from importance, and to establish what evidence is actually required before committing to anything.
External demand
A questionnaire arrives, or a contract clause does. Both ask for evidence of controls you may well run, but have never had to document in the shape being asked for.
Visibility gap
Systems, responsibilities, and existing safeguards are each known in parts, by different people. Nobody has assembled the whole picture, so priority follows whoever asked most recently.
Ownership gap
The assessment ends and the findings are real, but nobody owns the controls afterward. Reviews slip, evidence goes stale, and the next customer request starts the cycle again.
ISO/IEC 27001 · ISO/IEC 27002 · ISO/IEC 27017/27018 · SOC 2 · PCI DSS
DPDP Act, 2023 · GDPR · ISO/IEC 27701
ISO/IEC 42001 · NIST AI RMF · EU AI Act
NIST CSF · NIST SP 800-53 · NIST RMF · ISO 31000 · CIS Controls
CERT-In Directions · DORA · OWASP
Focused advisory services
Choose a focused engagement, or combine related disciplines around one business outcome. Scope is defined before the work begins.
View all servicesContinuity after the project
Cybersecurity as a managed function: Fractional CISO leadership, security architecture and control design, and security engineering for assessments, control operations and incident readiness — scoped to what your business needs.
Secalyx runs your cybersecurity function within the scope agreed in the statement of work (SOW).
Best if you do not yet have an internal security function.
Responsibility is divided deliberately: your team keeps context and access, Secalyx carries specific direction and operating discipline.
Best if you have a capable team with selected gaps.
How an engagement works
The sequence is simple to understand and disciplined enough to audit. The exact evidence, responsibilities, and outputs are agreed for each engagement.
Clarify the business trigger, boundaries, and success criteria.
Review what exists, test key assumptions, and distinguish fact from assertion.
Sequence actions around material risk, customer need, and operating capacity.
Transfer a sustainable capability, or run the agreed security-control scope.

The Experience Behind Secalyx
Founder & Principal Consultant
He holds CISSP (since 2009), CISM, CRISC, CISA, C|CISO, and CEH, and is a BSI-certified ISO/IEC 27001:2022 Lead Auditor and Lead Implementer.
Across a career spanning 25+ years, he has personally designed, built, and run cybersecurity and IT infrastructure from single-site environments to multi-city operations spanning Bengaluru, Mumbai, Delhi NCR, Pune, Indore, and international sites, supporting 5,000+ users.
He led security and technology programs that supported customer assurance assessments for Fortune 100 and Fortune 500 organizations across BFSI, healthcare, aviation, and other regulated environments. His current advisory work also includes data protection, security framework implementation, AI governance, and Fractional CISO leadership.
Insights
Why performance, risk, and control need three different indicators — not one number everyone agrees to watch.
Why mature security programs think in controls, not frameworks — and where “many frameworks, one operating model” breaks down if you take it too literally.
Why the real question was never “block AI or allow it” — and what changes when governance replaces fear.
Books
A practical four-volume reference connecting the domains cybersecurity leaders and senior practitioners are expected to lead.
Explore the series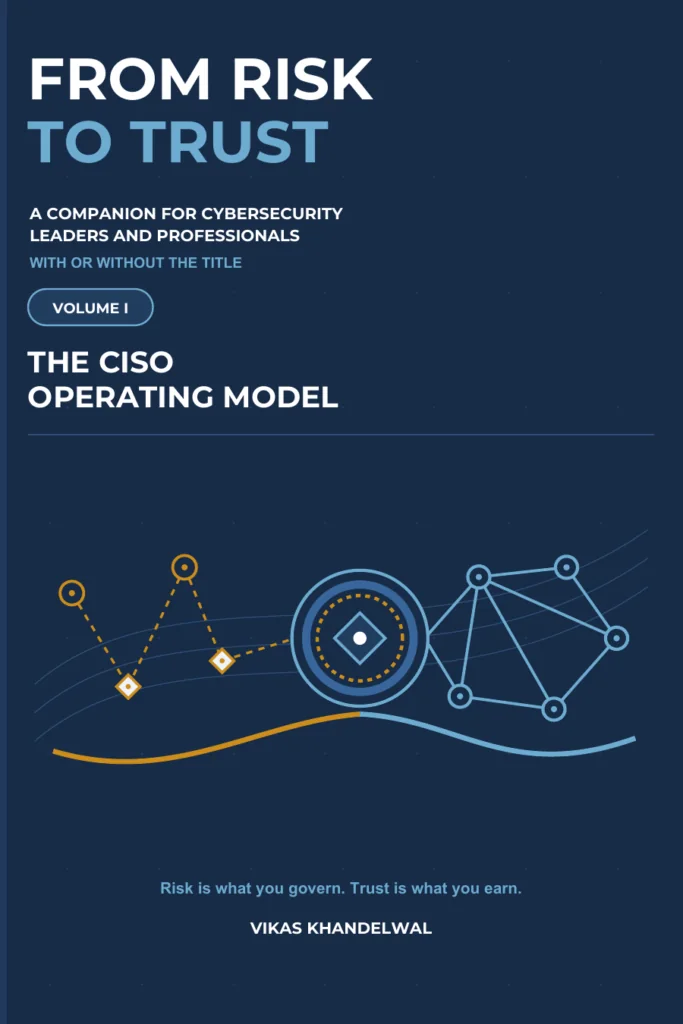
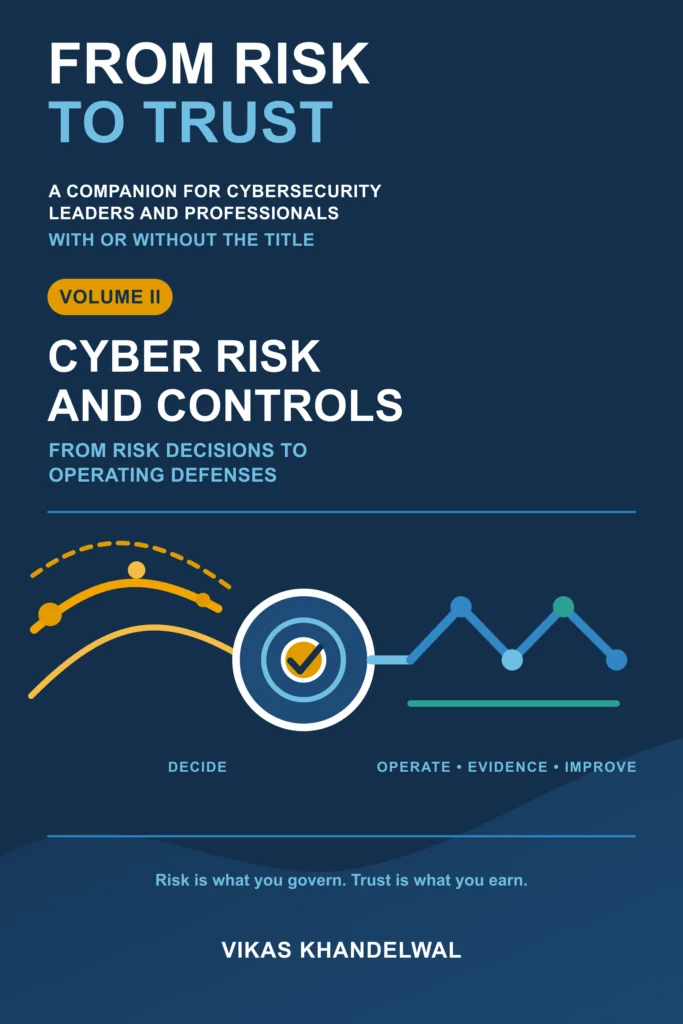
Ready to discuss the decision?
Share the pressure, requirement, or control question you are working through. A completed brief is not required.